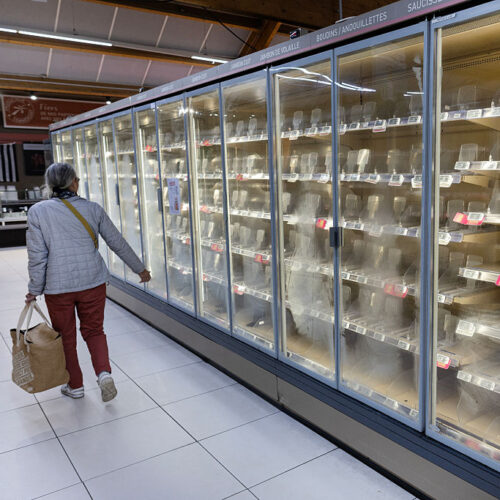
Earlier this week, a mass hack of refrigeration systems at an estimated 700 supermarkets throughout Europe caused them to suddenly malfunction, causing spoilage of untold tons of perishables and, in some cases, fires. As is now the norm, basic cybersecurity would have prevented it. French authorities say the systems, made up of entire fleets of refrigerators and freezers throughout a store, were hacked.
More specifically, Internet-connected controllers that allow technicians to remotely administer the store-wide systems were compromised. The unknown attackers responsible then activated defrosters long enough for the fridges to reach temperatures as high as 50° Celsius (122° Fahrenheit). By the time the mass compromise was discovered, food was spoiled, and in some cases their electrical systems caught fire.
Multiple security advisories and public research reports show that all three of the controller models reportedly hacked in the incident—sold by Danfoss of Denmark and Dixell and its parent company Copeland in the US—contained critical vulnerabilities that allow attackers to remotely log in to the devices with the same system rights as administrators. Until recently, Danfoss controllers, for instance, used a credential that changes each day. The password is generated by the publicly available firmware based on the date.
A hacker who takes the time to analyze the code can do the same thing on any device that hasn’t received a recent update. Daily passwords are identical across models located in hundreds or thousands of stores. A raft of critical vulnerabilities fixed in the past few months in Copeland/Dixel controllers also give similar remote access.
Extract — continue reading at the source.